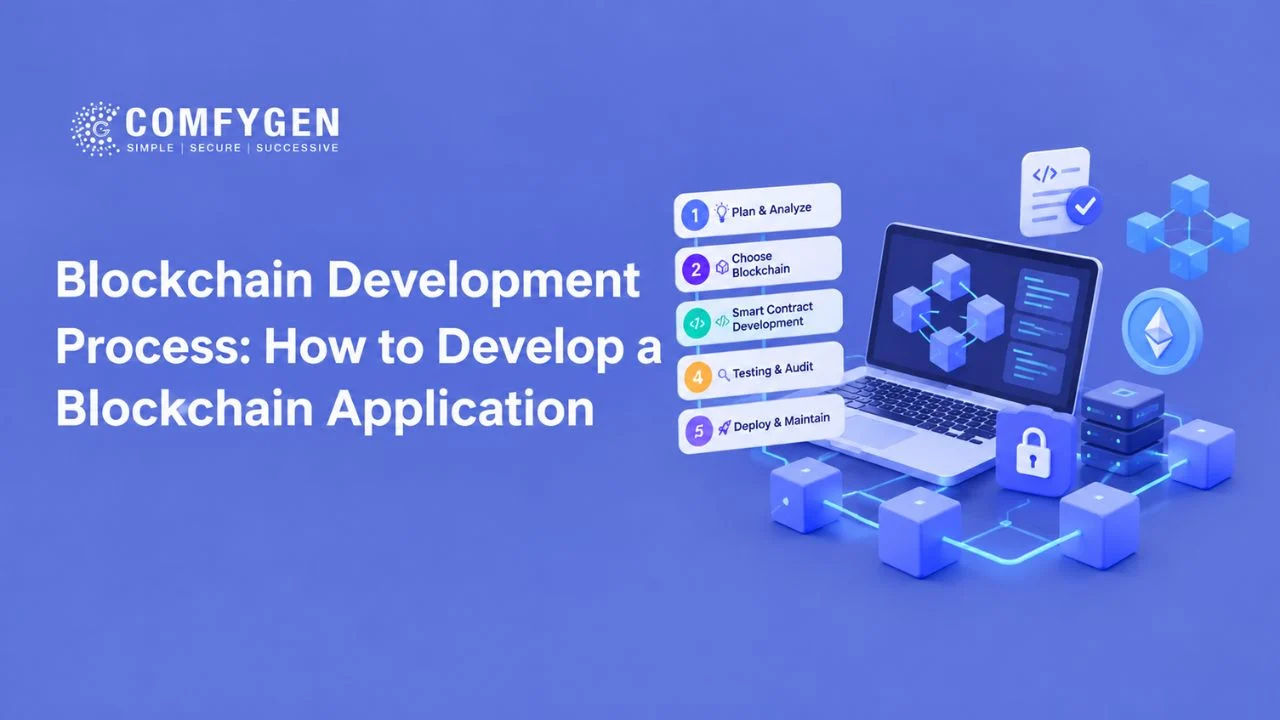


The blockchain development process runs through eight phases: use case validation, requirements definition, platform selection, architecture design, smart contract development, testing and security audit, deployment, and post-launch maintenance. Developing a blockchain application to production standard takes 4 to 9 months, depending on the chain you deploy to, how much custom contract logic you need, and the depth of security audit your use case demands.
This guide covers each phase in order: what happens, how long it takes, and which tools the team uses. It also covers how to set up a blockchain development environment from scratch, how to integrate with systems you already run, and what to consider if your project requires a new protocol rather than an application on an existing chain. It is written for founders, product managers, and technical leads scoping a project for the first time.
What Developing on the Blockchain Involves
Developing on the blockchain means building applications that store data on a distributed ledger rather than a central database. The ledger is replicated across a network of nodes, each holding an identical copy, and changes are accepted only when the network reaches consensus. Once a record is written, altering it would require rewriting every subsequent block on a majority of nodes simultaneously, which is what makes blockchain records practically immutable.
In practice the work splits into two distinct types, and conflating them is the most common scoping mistake.
Application-layer development means building on an existing chain. You write smart contracts that run on Ethereum, Polygon, Solana, or a permissioned network like Hyperledger Fabric, plus the frontend and backend that interact with them. This covers the majority of commercial projects: tokens, marketplaces, DeFi protocols, supply chain trackers, loyalty systems.
Protocol-layer development means building the chain itself — designing consensus rules, block structure, networking, and node software. This is rare, expensive, and only justified when no existing chain can meet your requirements for throughput, privacy, or governance, which is the point at which a custom blockchain build becomes the right call. The considerations specific to that path are covered in a dedicated section later in this guide.
Roughly nine out of ten business projects are application-layer. If you are scoping a first project, assume application-layer unless a specific constraint forces otherwise.
The 8 Phases of the Blockchain Development Process
| Phase |
What happens |
Typical duration |
Primary deliverable |
|---|---|---|---|
|
1. Use case validation |
Confirm blockchain is the right answer |
1–2 weeks |
Validation memo, go/no-go |
|
2. Requirements definition |
Functional, technical, compliance scope |
2–3 weeks |
Requirements doc, user flows |
|
3. Platform selection |
Chain, consensus, network type |
1 week |
Architecture decision record |
|
4. Architecture design |
Contract structure, data model, off-chain layer |
2–4 weeks |
Technical architecture, schema |
|
5. Smart contract development |
Write and compile contract logic |
4–10 weeks |
Contract codebase on testnet |
|
6. Testing and security audit |
Unit, integration, fuzz testing, external audit |
3–8 weeks |
Test coverage report, audit report |
|
7. Deployment |
Mainnet launch, verification, monitoring |
1–2 weeks |
Live contracts, verified source |
|
8. Maintenance |
Monitoring, upgrades, gas optimisation |
Ongoing |
Monthly ops reporting |
Phase 1: Validate the Use Case
The first question is not which chain to use. It is whether you need a blockchain at all.
A distributed ledger is the right tool when three conditions hold together:
- Multiple parties write to the same dataset and none of them fully trusts the others to control it
- The record needs to be verifiable by participants without a central authority vouching for it
- Disputes over history are expensive — in money, compliance exposure, or time
If a single organisation controls the data and participants trust it, a well-designed database with an audit log does the same job faster and for a fraction of the cost. Projects that fail this test tend to fail in production, because the team ends up paying blockchain costs for database benefits.
Validation deliverables:
- A written problem statement naming the parties, the shared data, and the trust gap
- A comparison against a centralised alternative, with cost and latency for both
- Identification of which data goes on-chain and which stays off-chain (almost never all of it)
- A proof of concept if the use case is novel — two to four weeks
Teams that are unsure whether their use case clears this bar usually start with a short blockchain consulting engagement rather than committing to a build.
Phase 2: Define Requirements
Requirements for blockchain projects carry constraints that conventional software does not. Three in particular drive the rest of the build.
Immutability changes how you design. Deployed contract code cannot be edited. If you expect the business logic to change, you must design an upgrade path at this stage — a proxy pattern, a modular contract structure, or a migration plan. Retrofitting upgradeability after deployment means redeploying and migrating state, which is expensive and risky.
Every write costs money. On a public chain, each state change consumes gas paid in the network’s native token. A design that writes a record per user action can be economically unviable at scale. This is a requirements-stage decision, not an optimisation to handle later.
On-chain data is permanent and public. On a public chain, anything you write is visible to everyone, forever. Personal data cannot go on-chain in any jurisdiction with a right-to-erasure provision, including under GDPR and India’s DPDP Act. The standard pattern is to store a cryptographic hash on-chain and the underlying data off-chain, which proves integrity without exposing content.
Requirements checklist:
|
Category |
Questions to answer |
|---|---|
|
Functional |
What transactions must the system support? Who initiates each one? |
|
Data |
What goes on-chain? What stays off-chain? How are they linked? |
|
Access |
Is the network open or permissioned? Who can read, write, validate? |
|
Economic |
Who pays gas — the user or the platform? What is the cost per transaction at projected volume? |
|
Upgrade |
Will the logic change? What governs an upgrade? |
|
Compliance |
Which regulations apply — KYC/AML, GDPR, DPDP, securities law if tokens are involved? |
|
Integration |
Which existing systems must connect? ERP, CRM, payment processor, identity provider? |
Phase 3: Select the Platform
Platform selection is driven by four variables: whether the network is public or permissioned, throughput requirements, transaction cost tolerance, and whether you need privacy between participants.
|
Platform |
Type |
Consensus |
Throughput (approx.) |
Contract language |
Best fit |
|---|---|---|---|---|---|
|
Public |
Proof of Stake |
~15–30 TPS base layer |
Solidity, Vyper |
Highest-value assets, deepest liquidity, maximum composability |
|
|
Public sidechain |
Proof of Stake |
~1,000+ TPS |
Solidity |
Consumer apps needing EVM compatibility at low gas cost |
|
|
Arbitrum / Base |
Public L2 rollup |
Ethereum settlement |
~2,000+ TPS |
Solidity |
DeFi and apps wanting Ethereum security with lower fees |
|
Public |
Proof of History + PoS |
~2,000–4,000 TPS sustained |
Rust, Anchor |
High-frequency consumer apps, payments, gaming |
|
|
Permissioned |
Pluggable (Raft) |
~1,000–3,000 TPS |
Go, JavaScript, Java |
Enterprise consortia, supply chain, trade finance |
|
|
R3 Corda |
Permissioned |
Notary-based |
Varies by deployment |
Kotlin, Java |
Regulated finance, where transactions must stay private between counterparties |
Throughput figures are indicative and vary considerably with network conditions, transaction type, and configuration. Treat them as orders of magnitude for comparison, not as service guarantees. Verify current figures against each network’s own documentation before committing.
The public versus permissioned decision
Choose a public blockchain when you need open participation, composability with other protocols, or a liquid asset. Accept that transactions are visible and costs fluctuate with network demand.
Choose a private or permissioned network when participants are known entities, data must stay confidential between specific parties, throughput needs to be predictable, or a regulator requires identifiable validators. Accept that you take on node operation and governance.
Hybrid designs are common in enterprise work: a permissioned chain for operational records, with periodic cryptographic commitments anchored to a public chain for third-party verifiability. Where several chains need to interoperate, a multichain architecture handles the bridging between them.
Comparing chains in more detail? See our breakdown of how to choose a blockchain platform for your business.
Phase 4: Design the Architecture
Blockchain architecture work covers four layers, and the balance between them determines both cost and performance.
The on-chain layer holds what must be trustless: ownership records, transaction logic, access rules, settlement. Keep this minimal. Every byte stored on a public chain is paid for at deployment and every operation is paid for at execution.
The off-chain data layer holds everything else: documents, media, user profiles, large datasets. Common patterns are IPFS or Arweave for content-addressed storage, and a conventional database for mutable application data. The on-chain record stores a hash that proves the off-chain data has not changed.
The integration layer connects the chain to the outside world. Oracles feed external data to contracts — prices, weather, delivery confirmations — because a contract cannot reach the internet by itself. For enterprise work, middleware connects the chain to ERP, CRM, and payment systems.
The application layer is the interface. Web and mobile frontends communicate with contracts through libraries like ethers.js, viem, or web3.js, and users sign transactions through a wallet. Where the interface is itself decentralised, this is where dApp development work sits, and the wallet layer may need a custom crypto wallet rather than a third-party one.
Architecture decisions worth documenting before coding starts:
- Contract structure: one monolithic contract or several modular ones
- Upgrade pattern: immutable, transparent proxy, UUPS, or diamond
- Access control: single owner, role-based, or multisig governance
- Gas strategy: who pays, and whether to use meta-transactions or account abstraction so end users do not need to hold the native token
- Key management: how private keys are generated, stored, and recovered — the most common source of real-world losses
Setting Up Your Blockchain Development Environment
Before any contract gets written, the team needs a working development environment. This sits at the start of Phase 5 and takes a developer under an hour on a clean machine. Getting it wrong costs far more later, because a misconfigured local chain or an unmanaged private key creates problems that only surface at deployment.
What a blockchain development environment consists of
|
Component |
Purpose |
Standard choice in 2026 |
|---|---|---|
|
Runtime |
Executes tooling and scripts |
Node.js LTS (for Hardhat), Rust toolchain (for Foundry) |
|
Package manager |
Dependency management |
npm, pnpm, or yarn |
|
Version control |
Code history, collaboration |
Git with GitHub, GitLab, or Bitbucket |
|
Development framework |
Compile, test, deploy |
Hardhat or Foundry |
|
Local blockchain node |
Fast testing without real gas |
Hardhat Network or Anvil (Foundry) |
|
Compiler |
Turns Solidity into bytecode |
solc, managed by the framework |
|
Contract libraries |
Audited building blocks |
OpenZeppelin Contracts |
|
Wallet |
Signs transactions, holds testnet funds |
MetaMask or Rabby, with a dedicated dev account |
|
RPC endpoint |
Connects to testnet and mainnet |
Alchemy, Infura, or QuickNode |
|
Editor tooling |
Syntax, linting, inline errors |
VS Code with a Solidity extension |
|
Secrets management |
Keeps keys out of the repository |
.env file, git-ignored, or a secrets manager |
Note that Ganache is no longer the local chain to use. It was archived alongside Truffle. Hardhat Network and Anvil both replace it and are actively maintained.
Setting up the environment step by step
- Install the runtime. Node.js LTS for a Hardhat project. For Foundry, install the Rust toolchain and then Foundry itself via foundryup.
- Initialise the project. npx hardhat init or forge init scaffolds the directory structure, a sample contract, and a test file.
- Install contract libraries. Add OpenZeppelin Contracts rather than writing token or access-control primitives yourself.
- Start the local chain. Hardhat Network runs automatically during tests; Anvil runs as a standalone process. Both give you funded test accounts instantly and mine blocks on demand, so there is no waiting and no real gas cost.
- Configure an RPC endpoint. Create a project with an RPC provider and store the URL as an environment variable. You need this for testnet deployment and for forking mainnet state during tests.
- Create a dedicated development wallet. Never reuse a personal wallet. Generate a fresh account for development and fund it from a public testnet faucet.
- Set up secrets handling. Private keys and RPC URLs go in a .env file that is listed in .gitignore from the first commit. Committed keys are one of the most common causes of drained development wallets, and once a key reaches a public repository it is compromised permanently.
- Add static analysis early. Install Slither and run it as part of the local workflow, not only before the audit. Catching issues during development is far cheaper than catching them in review.
- Configure networks. Add testnet and mainnet entries to the framework config, with the chain ID, RPC URL, and the account the deployment scripts will use.
- Set up block explorer verification. Add an explorer API key to the config so contracts can be verified automatically at deployment rather than manually afterwards.
Environment choices that cause problems later
- Not pinning the compiler version. Different solc versions produce different bytecode. Pin the version in the config so builds are reproducible and the audited bytecode matches what you deploy.
- Testing only against a local chain. A local node has no real network conditions, no competing transactions, and no live protocol state. Fork testing against a copy of mainnet catches integration problems that a clean local chain never will.
- Sharing one wallet across the team. Each developer needs their own development account. Shared keys make it impossible to attribute a transaction and multiply the exposure if one machine is compromised.
- Leaving verification until after launch. Unverified contracts on a block explorer are a visible trust problem and make independent review impossible.
Phase 5: Develop the Smart Contracts
Smart contracts are programs that execute automatically when their conditions are met. They are the core of application-layer work, and they are the part of the system that cannot be patched after the fact.
Language by platform:
|
Language |
Platform |
Notes |
|---|---|---|
|
Solidity |
Ethereum and all EVM chains |
The dominant language. Largest talent pool, most tooling, most audited reference code |
|
Vyper |
EVM chains |
Deliberately restricted feature set to reduce attack surface. Smaller ecosystem |
|
Rust |
Solana, Polkadot, NEAR |
Steeper learning curve, strong memory safety guarantees |
|
Go |
Hyperledger Fabric |
Used for Fabric chaincode in enterprise deployments |
|
Kotlin / Java |
R3 Corda |
Fits existing enterprise JVM environments |
Development practices that reduce audit findings:
- Build on audited libraries rather than writing primitives from scratch. OpenZeppelin’s contract library covers tokens, access control, and upgrade patterns, and is the most reviewed code in the ecosystem.
- Apply the checks-effects-interactions pattern consistently. Update internal state before making external calls. This is the primary structural defence against reentrancy, the vulnerability class behind many of the largest historical exploits.
- Keep functions short and single-purpose. Auditors charge for complexity, and complexity is where bugs live.
- Write tests as you write contracts, not afterwards. Target meaningful coverage of state-changing functions and every failure path.
- Optimise gas during development, not at the end. Storage layout, data types, and loop structure all affect cost, and changing them late means re-auditing.
For a code-level walkthrough, see how to build an Ethereum smart contract and smart contracts in business applications.
Phase 6: Test and Audit
This is where blockchain work diverges most sharply from conventional software. In a web application, a bug found in production is a deploy away from being fixed. In a deployed smart contract holding assets, it is a loss.
The scale is not theoretical. Web3 losses reached roughly $3.1 billion in the first half of 2025, with about $263 million of that attributable specifically to smart contract bugs.
The testing sequence:
- Unit tests — every function, including every revert condition and access restriction
- Integration tests — contracts interacting with each other and with external protocols
- Fork testing — run against a local copy of mainnet state to test real-world interactions with live protocols
- Fuzz and invariant testing — generate thousands of random inputs to find edge cases humans miss. Foundry’s built-in fuzzer has made this standard practice
- Static analysis — automated vulnerability scanning with Slither or Mythril before an auditor sees the code
- Testnet deployment — full system running on Sepolia, Amoy, or an equivalent testnet
- External security audit — independent review by a specialist firm
- Bug bounty — ongoing incentivised disclosure after launch, typically via Immunefi
Book the audit slot during phase 5. Reputable firms have waiting lists, and a project that finishes development with no audit booked will either delay launch or settle for a weaker reviewer. Protocols handling pooled funds should budget for the deeper review that DeFi smart contract development requires, since the attack surface is materially larger than for a standard token.
Phase 7: Deploy
Deployment is short but unforgiving.
Deployment checklist:
- Deploy to testnet first and run the full user journey end to end
- Verify and publish source code on the block explorer. Unverified contracts are a red flag to users and make independent review impossible
- Transfer ownership to a multisig wallet, never a single private key. A one-key admin is a single point of catastrophic failure
- Set up monitoring and alerting on contract events, balance changes, and unusual transaction patterns before announcing the launch, not after
- Document the deployment: addresses, constructor arguments, the exact commit hash audited, and the audit report itself
- If the contracts are upgradeable, test the upgrade path on testnet before mainnet launch
For permissioned networks, deployment also covers node provisioning across participating organisations, certificate authority setup, channel and access policy configuration, and an agreed governance process for future changes.
Phase 8: Maintain
Blockchain applications are not finish-and-forget. Ongoing work covers:
- Monitoring — contract activity, failed transaction rates, gas consumption, anomalous patterns
- Dependency tracking — vulnerabilities disclosed in libraries you depend on, including OpenZeppelin advisories
- Network upgrades — chains change. Ethereum’s upgrades have altered gas costs and opcode behaviour, and each one requires compatibility review
- Gas optimisation — transaction costs shift with network conditions, and designs that were economical at launch may need revisiting
- Frontend and infrastructure — RPC providers, indexers, and wallet integrations all require maintenance independent of the contracts
Budget 15 to 20 percent of original development cost per year for maintenance. For systems holding meaningful value, add an annual security review and an ongoing bug bounty.
Integrating Blockchain With Existing Systems
Most blockchain applications in production are not standalone. They connect to an ERP, a payment processor, an identity provider, or a database that will keep running after launch. Integration is where project timelines most often slip, because it is the one phase that depends on systems your team does not control.
Why a blockchain can not reach the outside world
A smart contract cannot make an HTTP request. Every node in the network has to execute the same code and arrive at the same result, and an external API that returns different data to different nodes at different moments would break consensus. Contracts are therefore deterministic and sealed off from external data by design.
Oracles solve this. An oracle is a service that writes external data onto the chain in a transaction, so the contract reads it from on-chain state rather than fetching it. The oracle becomes a trust dependency: a contract is only as reliable as the data feeding it, and oracle manipulation is a recognised attack vector in its own right.
|
Oracle type |
How it works |
Typical use |
Trust model |
|---|---|---|---|
|
Decentralised price feed |
Multiple independent nodes report, aggregated on-chain |
DeFi collateral valuation, lending, derivatives |
Distributed across node operators |
|
Single-source API oracle |
One operator writes data from a named API |
Enterprise workflows with a known data owner |
Trust the single operator |
|
Hardware / IoT oracle |
Sensor or device writes readings via a gateway |
Supply chain, cold chain, logistics |
Trust the device and its gateway |
|
Human / consensus oracle |
Participants attest to an outcome, resolved by vote |
Insurance claims, prediction markets, dispute resolution |
Trust the attesting group |
Chainlink is the most widely deployed decentralised oracle network and the default choice for public-chain price data. For permissioned enterprise networks, a single-source oracle operated by the data owner is often appropriate, because the trust assumption already exists in the business relationship.
Connecting separate blockchains
Projects that span more than one chain need an interoperability layer. Three approaches dominate.
|
Approach |
What it does |
Best for |
|---|---|---|
|
Bridges |
Lock an asset on one chain, mint a representation on another |
Moving tokens between EVM chains |
|
Relay and hub networks (Cosmos IBC, Polkadot) |
Purpose-built messaging between chains in a shared ecosystem |
Projects designing for multi-chain from the start |
|
Payment interoperability protocols (Interledger) |
Route value across ledgers, including non-blockchain systems |
Cross-border payments touching banking rails |
Bridges deserve particular caution. They hold locked assets, which makes them among the most frequently exploited components in the ecosystem. Several of the largest crypto losses on record have been bridge compromises. If your architecture needs a bridge, use an established one with a public audit history rather than building your own, and treat it as a dependency you are inheriting risk from.
Integration patterns for existing systems
|
Pattern |
How it works |
Best for |
Relative effort |
|---|---|---|---|
|
API and middleware layer |
A service sits between the chain and existing systems, translating between them |
Most enterprise projects |
Moderate |
|
Hybrid — off-chain record, on-chain proof |
Existing system stays the system of record; hashes of key events are committed on-chain |
Adding verifiability without migration |
Low to moderate |
|
Permissioned chain inside the enterprise boundary |
The network runs within existing infrastructure and security controls |
Consortia, regulated industries |
High |
|
Tokenisation of existing assets |
Physical or financial assets get an on-chain representation |
Trade finance, real estate, carbon credits |
High, with legal review |
The hybrid pattern is the one most organisations should start with. It delivers a tamper-evident audit trail without migrating a working system, and it keeps the blast radius small if the project does not progress. Full tokenisation is the largest commitment, because the legal status of the on-chain representation has to be established before the technical work means anything.
What integration adds to the budget
Integration is routinely under-scoped. Each external system you connect adds cost independent of the contracts themselves:
- Middleware and API layer: typically 10–20% of total project cost
- Each additional enterprise system (ERP, CRM, payment processor): adds its own discovery, credentialing, and testing cycle
- Oracle setup and ongoing feed costs: small to build, recurring to run
- Data synchronisation and reconciliation logic: the quiet cost driver, because on-chain and off-chain state will diverge and something has to resolve it
Scope integration during Phase 2 and architect it in Phase 4. Discovering an integration requirement during Phase 5 is one of the most common causes of overrun.
Blockchain Application Development Tools in 2026
The tooling landscape changed significantly in late 2023. Consensys sunset Truffle and Ganache, directing developers to Hardhat, Foundry, Remix, Thirdweb and OpenZeppelin, and the codebases were moved to public archives in December 2023. Any guide still recommending Truffle as a primary framework is out of date.
|
Category |
Tool |
What it does |
Cost |
|---|---|---|---|
|
Framework |
Hardhat |
JavaScript/TypeScript development environment, testing, deployment scripting, mainnet forking |
Free, open source |
|
Framework |
Foundry |
Rust-based toolkit. Tests written in Solidity, built-in fuzzing, fastest compile and test cycle |
Free, open source |
|
IDE |
Remix |
Browser-based IDE. No local setup. Best for learning, quick prototypes, and inspecting deployed contracts |
Free |
|
Libraries |
OpenZeppelin Contracts |
Audited implementations of tokens, access control, and upgrade patterns |
Free, open source |
|
Static analysis |
Slither |
Automated vulnerability detection across 90+ detector patterns |
Free, open source |
|
Static analysis |
Mythril |
Symbolic execution to find exploitable states |
Free, open source |
|
Node access |
Alchemy, Infura, QuickNode |
Managed RPC endpoints so you don’t run your own node |
Free tier, then usage-based |
|
Indexing |
The Graph, Ponder |
Query on-chain data efficiently for frontends |
Free tier, then usage-based |
|
Frontend |
ethers.js, viem, wagmi |
Connect web apps to contracts and wallets |
Free, open source |
|
Enterprise |
Hyperledger Fabric SDKs |
Chaincode development and network administration for permissioned deployments |
Free, open source |
|
Monitoring |
OpenZeppelin Defender, Tenderly |
Transaction monitoring, alerting, automated response |
Free tier, then paid |
Choosing between Hardhat and Foundry: Hardhat suits teams whose backend is already JavaScript or TypeScript and who want one language across the stack. Foundry suits teams writing tests in Solidity who want faster execution and native fuzzing. Many teams run both — Foundry for testing, Hardhat for deployment scripting. Neither choice is wrong, and both are actively maintained.
Key Considerations When Designing a New Blockchain Protocol
Everything above assumes you are building on an existing chain. A small number of projects genuinely need their own protocol — a new chain with its own consensus, block structure, and node software. This section covers what that decision involves.
When a new protocol is justified
Designing a new protocol is warranted when an existing chain cannot meet a hard requirement:
- Throughput or latency beyond what available chains deliver, where Layer 2 options do not close the gap
- Data confidentiality between specific participants that no public chain can provide
- Governance control that a regulator requires and a permissionless network cannot offer
- A novel consensus or economic model that is the product itself, rather than a means to deliver it
If none of these apply, building on an established chain is faster, cheaper, and inherits an ecosystem of tooling, auditors, wallets, and users that a new chain has to build from zero. The most common and most expensive mistake at this stage is choosing a new protocol for reasons of control or branding when an application on an existing chain would have met every actual requirement.
The eight design decisions
|
Decision |
What it determines |
Where it goes wrong |
|---|---|---|
|
Consensus mechanism |
How nodes agree, and how quickly finality is reached |
Choosing a mechanism whose security assumptions do not match the validator set you can realistically recruit |
|
Validator set and Sybil resistance |
Who can produce blocks, and what stops one party running many |
A small permissioned validator set that is decentralised in name only |
|
State model |
Account-based or UTXO |
Picking one without modelling the actual transaction patterns |
|
Execution environment |
EVM-compatible or a custom virtual machine |
A custom VM means no existing tooling, no existing auditors, and no existing developer pool |
|
Block parameters |
Block time, block size, finality |
Optimising for headline throughput at the cost of reorg safety |
|
Economic and incentive design |
What validators earn, what users pay, what attacks cost |
Incentives that are rational to abandon under stress, which is when they matter |
|
Governance and upgrade mechanism |
How the protocol changes once live |
No upgrade path, or one controlled by a single key |
|
Networking layer |
Peer discovery, propagation, partition behaviour |
Underestimating propagation delay at geographic scale |
Build from a framework, not from nothing
Almost nobody writes a chain from first principles. Three frameworks supply consensus, networking, and state management so the team only implements what is genuinely novel.
|
Framework |
Model |
Best fit |
|---|---|---|
|
Modular runtime, pluggable consensus, optional Polkadot connection |
Custom public or consortium chains wanting an upgrade path and ecosystem access |
|
|
Cosmos SDK |
Application-specific chains with Tendermint consensus and IBC |
Sovereign chains that need to interoperate with others |
|
Hyperledger Fabric |
Permissioned, pluggable consensus, private channels |
Enterprise consortia where participants are known and data must stay partitioned |
Using a framework is not a shortcut. It removes the parts that are solved problems so the team’s effort goes into the parts that are not.
What protocol-layer work actually costs
Protocol design and implementation starts around $250,000 and runs considerably higher once validator recruitment, economic modelling, and external security review are included. Timelines run 9 to 18 months before a network is production-ready.
The cost that teams consistently miss is everything after launch: a chain with no block explorer, no wallet support, no indexer, and no auditors familiar with its VM is a chain nobody can build on. Budget for ecosystem tooling as a first-class line item, not an afterthought.
What Developing a Blockchain Application Costs
Cost is driven by contract complexity, chain choice, audit depth, and team location. The ranges below cover development through launch and exclude ongoing maintenance.
|
Project tier |
Scope |
Cost range |
Timeline |
|---|---|---|---|
|
Proof of concept |
Single contract, testnet only, no audit, basic interface |
$8,000 – $20,000 |
2–4 weeks |
|
MVP |
Core contracts, standard audit, functional frontend, mainnet launch |
$40,000 – $90,000 |
3–5 months |
|
Production application |
Multiple contracts, full audit, admin panel, integrations, monitoring |
$90,000 – $250,000 |
5–9 months |
|
Permissioned chain or protocol-layer build, multi-party governance, compliance layer |
$250,000 – $600,000+ |
9–18 months |
The factors that move the number most:
- Audit scope — the single largest variable. A DeFi protocol handling pooled funds needs a far deeper review than a loyalty token
- Chain — Solana and non-EVM chains cost more to build and audit because the talent pool is smaller
- Upgradeability — proxy patterns add development time and audit surface
- Integrations — each external system, oracle, or payment rail adds cost independent of the contracts
- Compliance — KYC/AML, securities analysis, and jurisdictional legal review are separate budget lines that teams routinely forget to include
- Team location — India-based blockchain teams typically bill $25 to $65 per hour against $100 to $200 for US agencies. The qualifier that matters is demonstrated audit-passing track record, not the rate. Our breakdown of what it costs to hire Ethereum developers from India covers the rate comparison in detail
For a line-by-line breakdown by component, see our full guide to blockchain development cost.
Who You Need on a Blockchain Development Team
|
Role |
Responsibility |
When they join |
|---|---|---|
|
Blockchain architect |
Chain selection, contract structure, data model |
Phase 3–4 |
|
Smart contract developer |
Contract logic, gas optimisation, tests |
Phase 5–6 |
|
Backend developer |
Off-chain services, indexing, integrations |
Phase 4–7 |
|
Frontend developer |
Interface, wallet connection, transaction UX |
Phase 5–7 |
|
QA engineer |
Test coverage, edge cases, testnet validation |
Phase 5–7 |
|
Security auditor (external) |
Independent contract review |
Phase 6 |
|
DevOps engineer |
Node infrastructure, CI/CD, monitoring |
Phase 6–8 |
|
Project manager |
Scope, timeline, audit scheduling, stakeholder reporting |
Phase 1–8 |
A minimum viable team for an MVP is four people: an architect who also writes contracts, a full-stack developer, a QA engineer, and a project manager, plus an external auditor. Teams smaller than this tend to skip testing or architecture, and both show up later as cost.
Organisations that need to scale a team for a fixed engagement rather than build one permanently can hire blockchain developers on a dedicated basis for the phases that need them.
Common Failure Points
Five patterns account for most blockchain projects that fail or overrun.
Putting data on-chain that shouldn’t be there. Large payloads, personal data, or frequently-changing records. The result is costs that scale badly and compliance exposure that cannot be undone, because on-chain data cannot be deleted.
Skipping the audit to make a launch date. The economics never work. The average loss per smart contract exploit over the past four years has been roughly $1.9 million — multiples of any audit fee.
Designing for immutability, then needing changes. Decide the upgrade strategy in phase 4. Retrofitting it means redeploying and migrating state.
Ignoring key management. More value has been lost to compromised or lost keys than to contract bugs. Multisig for admin functions, hardware wallets for treasury, documented recovery procedures.
Building a token before building a reason for it. A token adds securities-law exposure, market-making obligations, and ongoing governance. If the application works without one, ship it without one. Where a token genuinely is the product, treat crypto token development as its own workstream with its own legal review — our guide on how to launch your own cryptocurrency covers that path separately.
Build Your Blockchain Project With Comfygen
Comfygen provides blockchain development services for clients across the US, UK, UAE, Canada, Singapore, and India, covering smart contract development, DeFi protocols, token systems, wallets, and permissioned enterprise networks.
Our blockchain practice works across Ethereum and EVM chains, Solana, Polygon, Hyperledger Fabric, and Substrate, using Hardhat and Foundry with OpenZeppelin libraries as standard, and we coordinate independent third-party security audits as part of every mainnet build.
FAQ’s
A proof of concept takes two to four weeks. An MVP with audited contracts and a working interface takes three to five months. A production application with multiple contracts and external integrations takes five to nine months. Enterprise permissioned networks take nine to eighteen months. These timelines include security audit and testnet validation, both of which are required before mainnet launch. Solidity is the most widely used language, running on Ethereum and every EVM-compatible chain including Polygon, Arbitrum, and Base. Rust is used for Solana, Polkadot, and NEAR. Go is used for Hyperledger Fabric chaincode, and Kotlin or Java for R3 Corda. Solidity has the largest talent pool and the most audited reference code available. A working environment needs a runtime (Node.js for Hardhat, the Rust toolchain for Foundry), a development framework, a local blockchain node such as Hardhat Network or Anvil, the Solidity compiler managed by that framework, OpenZeppelin contract libraries, a dedicated development wallet funded from a testnet faucet, an RPC endpoint from a provider such as Alchemy or Infura, and a git-ignored .env file for keys. Setup takes under an hour. Ganache is no longer used, having been archived alongside Truffle in 2023. Choose a public chain when you need open participation, composability with other protocols, or a tradable asset, and you can accept that transactions are publicly visible. Choose a permissioned network when participants are known entities, data must stay confidential between specific parties, throughput needs to be predictable, or a regulator requires identifiable validators. Hybrid designs that anchor a permissioned chain to a public one are common in enterprise deployments. A new protocol is justified only when an existing chain cannot meet a hard requirement: throughput beyond what Layer 2 options deliver, confidentiality between specific participants, governance a regulator requires, or a novel consensus model that is the product itself. Otherwise, building on an established chain is faster and inherits existing tooling, auditors, wallets, and users. Protocol work starts around $250,000 and takes 9 to 18 months, with ecosystem tooling — explorers, wallets, indexers — as a separate cost most teams underestimate. Through an oracle. Smart contracts cannot make HTTP requests, because every node must execute identical code and reach identical results, and an external API returning different data to different nodes would break consensus. An oracle writes external data onto the chain in a transaction, which the contract then reads from on-chain state. Chainlink is the most widely deployed decentralised oracle network; permissioned enterprise networks often use a single-source oracle operated by the data owner. Scaling is handled at three levels. At the chain level, deploying to a Layer 2 rollup or a high-throughput chain raises the transaction ceiling. At the architecture level, moving data and computation off-chain and committing only proofs on-chain reduces the load that has to reach consensus at all. At the contract level, optimising storage layout, data types, and loop structure lowers gas per transaction. Architecture-level decisions deliver the largest gains and are the hardest to retrofit, which is why throughput requirements belong in Phase 2. The main technical risks are smart contract vulnerabilities, compromised private keys, and oracle manipulation. The main commercial risks are regulatory exposure — particularly where tokens may be treated as securities — unviable transaction economics at scale, and building on a chain whose ecosystem declines. Technical risks are addressed through audit, multisig key management, and reputable oracle providers. Commercial risks need legal review and economic modelling during phases 1 and 2.How long does blockchain development take?
Which programming language is used for blockchain development?
What do you need to set up a blockchain development environment?
Should I build on a public or private blockchain?
When is it worth designing a new blockchain protocol instead of building on an existing chain?
How does a blockchain application connect to an external data source?
How do you scale a blockchain application?
What are the main risks in a blockchain project?
Mr. Saddam Husen, (CTO)
Mr. Saddam Husen, CTO at Comfygen, is a renowned Blockchain expert and IT consultant with extensive experience in blockchain development, crypto wallets, DeFi, ICOs, and smart contracts. Passionate about digital transformation, he helps businesses harness blockchain technology’s potential, driving innovation and enhancing IT infrastructure for global success.